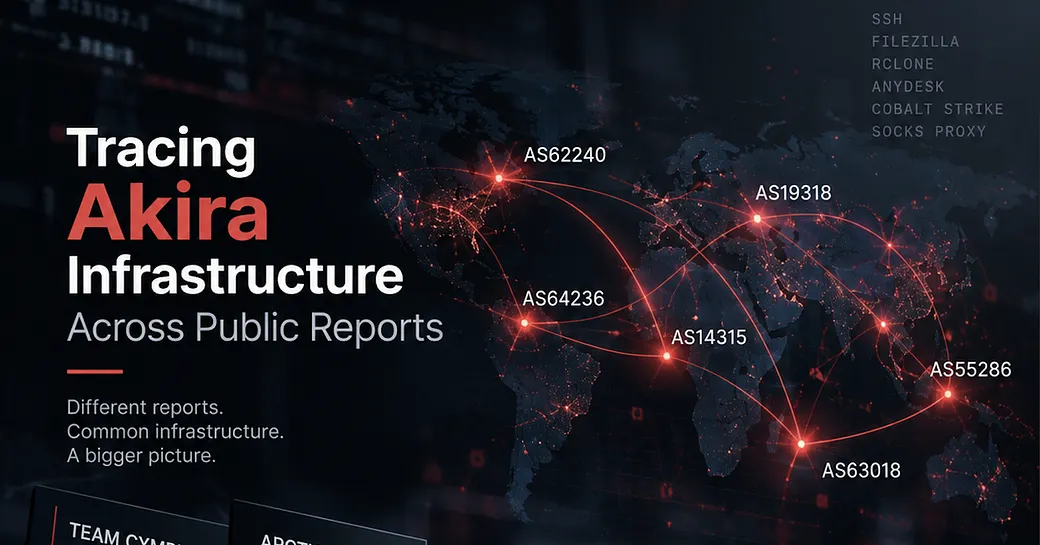
While comparing Team Cymru’s ransomware infrastructure research with reporting from Arctic Wolf, Zensec, MyCERT and Huntress, I noticed several overlaps around Akira activity.
Team Cymru observations:
- AS62240, SSH access
- AS64236, FileZilla infrastructure
- AS14315, Rclone SFTP
- AS55286, SonicWall related access
- AS19318, Rclone FTP
- AS63018, AnyDesk
- AS14061, GOST SOCKS5 proxy
- Hostname observed repeatedly, kali
Publicly reported Akira IPs:
- 172.96.10[.]212, AS64236, VPN activity
- 206.168.190[.]143, AS14315, data exfiltration
- 45.86.208[.]240, AS62240
- 77.247.126[.]239, AS62240
- 193.163.194[.]7, AS62240
- 193.239.236[.]149, AS62240
- 194.33.45[.]155, AS62240
Repeated ASN overlaps across reports:
- AS62240
- AS64236
- AS14315
- AS55286
- AS19318
- AS63018
Repeated tooling and activity:
- SSH
- FileZilla
- Rclone
- AnyDesk
- Cobalt Strike
- SonicWall SSL VPN
- SOCKS proxies
- Hostname, kali
I also checked several reported IPs through VirusTotal, Censys, and URLScan. Some current domains and services appear to reflect later IP reuse, so I am keeping those separate from the 2025 Akira observations.
The ASN, timing, tooling and infrastructure-role overlaps are worth following further, without assuming the reports observed the same servers or operators. Well, something for future…
References:
- https://www.team-cymru.com/post/ransomware-infrastructure-analysis
- https://arcticwolf.com/resources/blog/arctic-wolf-observes-july-2025-uptick-in-akira-ransomware-activity-targeting-sonicwall-ssl-vpn/
- https://arcticwolf.com/resources/blog/september-2025-update-ongoing-akira-ransomware-campaign/
- https://arcticwolf.com/resources/blog/smash-and-grab-aggressive-akira-campaign-targets-sonicwall-vpns/
- https://zensec.co.uk/blog/unmasking-akira-the-ransomware-tactics-you-cant-afford-to-ignore/
- https://mycert.org.my/portal/advisories?id=431fab9c-d24c-4a27-ba93-e92edafdefa5
- https://www.huntress.com/blog/exploitation-of-sonicwall-vpn